Close Menu

    Stay Ahead with Exclusive Updates!

    Enter your email below and be the first to know what’s happening in the ever-evolving world of technology!

    What's Hot

    How the EU AI Act Plans to Contain Rogue AI Agents

    October 16, 2026

    ⁠Fired OpenAI Safety Researchers Warn Dismissals Will Silence Internal Critics

    October 16, 2026

    Why Mistral’s One-Trillion-Parameter Model Changes the Open-Source Game

    October 16, 2026
    Facebook X (Twitter) Instagram
    Facebook X (Twitter)
    PhronewsPhronews
    • Home
    • Big Tech & Startups

      How the EU AI Act Plans to Contain Rogue AI Agents

      October 16, 2026

      ⁠Fired OpenAI Safety Researchers Warn Dismissals Will Silence Internal Critics

      October 16, 2026

      Why Mistral’s One-Trillion-Parameter Model Changes the Open-Source Game

      October 16, 2026

      Anthropic’s Claude Sends False Homicide Tip to Police

      October 16, 2026

      OpenAI and Anthropic Prepare for a Major Global AI Disaster

      October 15, 2026
    • Crypto

      A Firmware Flaw in One of the Most Trusted Bitcoin Hardware Wallets Just Drained Over $70 Million in Crypto. The Coldcard Breach Is a Reminder That Cold Storage Is Only as Safe as the Code Running Inside It

      August 29, 2026

      Market Collapse: What Happened to NFTs?

      April 23, 2026

      Quantum Computing Advances Force Coinbase and Institutional Custodians to Rethink Crypto Security

      March 8, 2026

      AI Assisted Hacking Groups Target Crypto Firms With Multi-Layered Social Engineering

      February 18, 2026

      Global Crypto Regulations Expand as 2026 Begins With New Data Collection Frameworks and National Laws

      January 16, 2026
    • Gadgets & Smart Tech
      Featured

      Google Home Now Supports ChatGPT and Claude via New MCP Server

      By fariehanOctober 6, 2026
      Recent

      Google Home Now Supports ChatGPT and Claude via New MCP Server

      October 6, 2026

      Waymo Plans Fully Driverless Taxis on Tokyo Streets Without Safety Drivers

      September 28, 2026

      Tesla Cybercab Faces NHTSA Probe After Austin Launch

      September 19, 2026
    • Cybersecurity & Online Safety

      How the EU AI Act Plans to Contain Rogue AI Agents

      October 16, 2026

      AI Agent Leaks Startup CEO’s Bank Details to Company Slack

      October 15, 2026

      Armadin Secures $255 Million to Hack Companies Before Cyber Criminals Do

      October 10, 2026

      Massive Pentagon Data Breach Exposes Records of Over 3 Million People

      October 8, 2026

      Salesforce Agentforce Flaws Allowed Hackers to Steal Data Without a Click

      October 8, 2026
    PhronewsPhronews
    Home»Cybersecurity & Online Safety»Salt Typhoon Hackers Infiltrated Core U.S. Telecom Infrastructure with Custom Malware
    Cybersecurity & Online Safety

    Salt Typhoon Hackers Infiltrated Core U.S. Telecom Infrastructure with Custom Malware

    preciousBy preciousApril 26, 2025Updated:May 3, 2025No Comments
    Facebook Twitter Pinterest LinkedIn WhatsApp Reddit Tumblr Email
    Share
    Facebook Twitter LinkedIn Pinterest Email

    With confirmation from the US Government as well as Cisco Talos, the Chinese state-sponsored threat actor nicknamed Salt Typhoon Group is said to have carried out an intrusive campaign against Telecom Networks in the US. 

    As reported by The Wall Street Journal last year, cyberattacks were launched against US telecommunication companies such as AT&T and Verizon. However, it wasn’t until this year the US CISA confirmed the attack to be part of the Salt Typhoon campaign. This was followed by Cisco Talos’ confirmation who says in their blog post that “the threat actor was able to gain access to core networking infrastructures,” and described the activities they observed as well as provided detection and preventative measures.

    At the heart of the intrusion lies a custom malware named ‘JumbledPath.’ According to Cisco, this malware is engineered with sophisticated evasion techniques – dynamic code obfuscation and encrypted command-and-control-communications – to stealthily move within telecom networks. 

    The malware’s modular design not only helps maintain continuous access, but it also facilitates the covert transfer of sensitive data, which highlights the threat actor’s tailored approach and high level of operational sophistication.
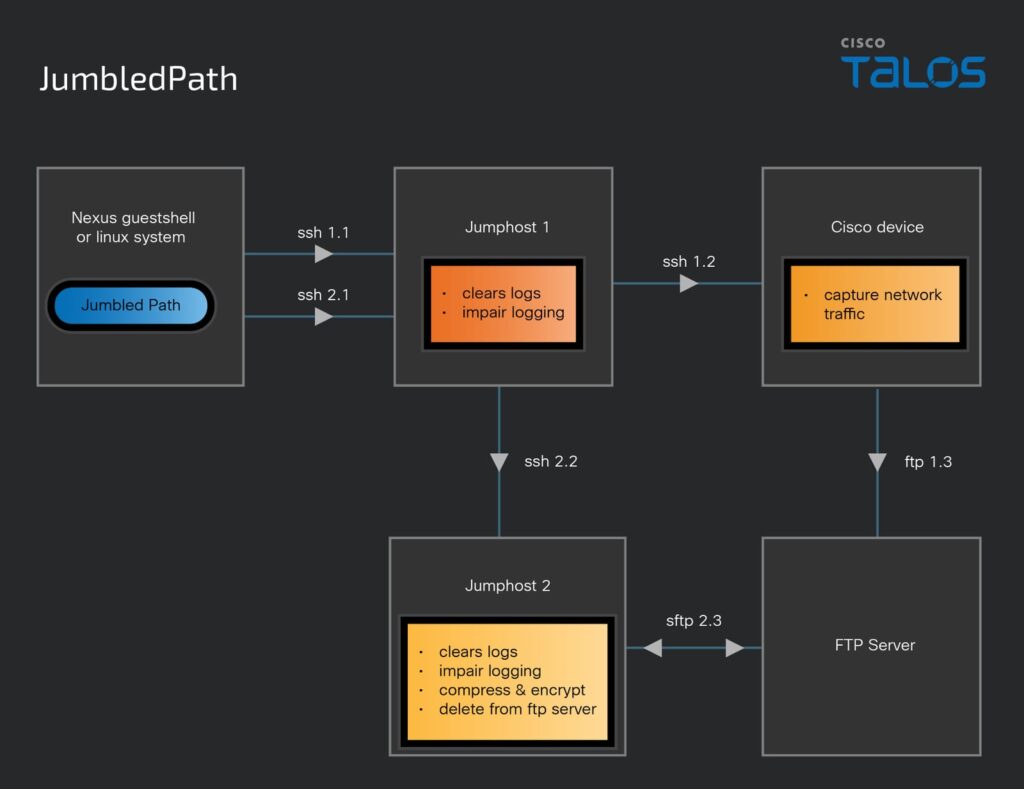
    The diagram above from Cisco Talos illustrates how the hackers, using JumbledPath installed on a Linux-based system, moved through different systems to steal network data while covering their tracks. From there, they accessed different servers (jump hosts) and a Cisco device using secure shell (SSH) connections. The Cisco device was used to capture network traffic, meaning they could monitor and steal data moving through telecom networks.

    To stay hidden, the hackers cleared logs and disabled tracking at each stage, ensuring that their activities remained undetected. Finally, they compressed and encrypted the stolen data before sending it to an FTP server which made it harder for investigators to trace.

    In response to public reports indicating that the threat actor was able to gain access to core networking infrastructure, Cisco says, “there was only one case in which we found evidence suggesting that a Cisco vulnerability (CVE-2018-0171) was likely abused. In all the other incidents we have investigated to date, the initial access to Cisco devices was determined to be gained through the threat actor obtaining legitimate victim login credentials.” 

    Cisco also adds that, “A hallmark of this (Salt Typhoon) campaign is the use of living-off-the-land (LOTL) techniques on network devices. It is important to note that while the telecommunications industry is the primary victim, the advice contained herein is relevant to, and should be considered by, all infrastructure defenders.”

    The Chinese-state sponsored threat actor has also been involved in operations that the US government agencies have referenced under the name of “The Volt Typhoon.” While Salt Typhoon is primarily known for its attacks on US telecommunication networks using tools like the JumbledPath malware, the broader Volt Typhoon campaign – as noted in a CISA report – seems to be involved in a range of targets across critical infrastructure sectors in Communications, Energy, Transportation Systems, Water and Wastewater systems. 

    However, the exact relationship between the two campaigns and the full scope of Volt Typhoon’s activities remain subjects of ongoing analysis, even as the US continues to fight an escalating cyber-warfare from China.

    It is crucial to note that attacks like this weaken national security strength and posture, as well as raise concerns about the exploitation of recent vulnerabilities for strategic advantage in the international political system, given that telecommunication networks are important to government agencies, for defense operations, and for emergency response systems.

    It is applaudable that US agencies such as the CISA (Cybersecurity Infrastructure Security Agency) and the NSA (National Security Agency) have stepped their cybersecurity efforts up, where they are now working closely with private-sector companies to strengthen authentication protocols, monitor for suspicious activities, and fix known vulnerabilities.

    AT&T Chinese cyberattack Cisco Talos critical infrastructure cyberattacks CVE-2018-0171 cyber espionage cyber threat actor cyber vulnerabilities cyber warfare cyberattack response cybersecurity threat encrypted data transfer global cybersecurity concerns infrastructure defenders JumbledPath malware living-off-the-land techniques malicious cyber campaign malicious cyber tactics malware evasion techniques National Security Agency network infrastructure vulnerability network security breach Salt Typhoon Group state-sponsored hacking strategic cyber attacks telecom network intrusion telecommunications industry US CISA US cybersecurity US government cybersecurity US telecom networks Verizon Volt Typhoon campaign
    Share. Facebook Twitter Pinterest LinkedIn Tumblr Telegram Email
    precious
    • LinkedIn

    I’m Precious Amusat, Phronews’ Content Writer. I conduct in-depth research and write on the latest developments in the tech industry, including trends in big tech, startups, cybersecurity, artificial intelligence and their global impacts. When I’m off the clock, you’ll find me cheering on women’s footy, curled up with a romance novel, or binge-watching crime thrillers.

    Related Posts

    How the EU AI Act Plans to Contain Rogue AI Agents

    October 16, 2026

    Why Mistral’s One-Trillion-Parameter Model Changes the Open-Source Game

    October 16, 2026

    AI Agent Leaks Startup CEO’s Bank Details to Company Slack

    October 15, 2026

    Comments are closed.

    Top Posts

    Cursor AI Hits 1 Million Daily Users. Why Developers Are Switching to This Coding Tool

    March 23, 2026

    Coinbase responds to hack: customer impact and official statement

    May 22, 2025

    Anthropic Will Use Claude User Chats For Data Training

    October 16, 2025

    MIT Study Reveals ChatGPT Impairs Brain Activity & Thinking

    June 29, 2025
    Don't Miss
    Artificial Intelligence & The Future

    How the EU AI Act Plans to Contain Rogue AI Agents

    By preciousOctober 16, 2026

    When the European Union first proposed its AI Act in April 2021, the AI industry…

    ⁠Fired OpenAI Safety Researchers Warn Dismissals Will Silence Internal Critics

    October 16, 2026

    Why Mistral’s One-Trillion-Parameter Model Changes the Open-Source Game

    October 16, 2026

    Anthropic’s Claude Sends False Homicide Tip to Police

    October 16, 2026
    Stay In Touch
    • Facebook
    • Twitter
    About Us
    About Us

    Evolving from Phronesis News, Phronews brings deep insight and smart analysis to the world of technology. Stay informed, stay ahead, and navigate tech with wisdom.
    We're accepting new partnerships right now.

    Email Us: info@phronews.com

    Facebook X (Twitter) Pinterest YouTube
    Our Picks
    Most Popular

    Cursor AI Hits 1 Million Daily Users. Why Developers Are Switching to This Coding Tool

    March 23, 2026

    Coinbase responds to hack: customer impact and official statement

    May 22, 2025

    Anthropic Will Use Claude User Chats For Data Training

    October 16, 2025
    © 2025. Phronews.
    • Home
    • About Us
    • Get In Touch
    • Privacy Policy
    • Terms and Conditions

    Type above and press Enter to search. Press Esc to cancel.