Close Menu

    Stay Ahead with Exclusive Updates!

    Enter your email below and be the first to know what’s happening in the ever-evolving world of technology!

    What's Hot

    How the EU AI Act Plans to Contain Rogue AI Agents

    October 16, 2026

    ⁠Fired OpenAI Safety Researchers Warn Dismissals Will Silence Internal Critics

    October 16, 2026

    Why Mistral’s One-Trillion-Parameter Model Changes the Open-Source Game

    October 16, 2026
    Facebook X (Twitter) Instagram
    Facebook X (Twitter)
    PhronewsPhronews
    • Home
    • Big Tech & Startups

      How the EU AI Act Plans to Contain Rogue AI Agents

      October 16, 2026

      ⁠Fired OpenAI Safety Researchers Warn Dismissals Will Silence Internal Critics

      October 16, 2026

      Why Mistral’s One-Trillion-Parameter Model Changes the Open-Source Game

      October 16, 2026

      Anthropic’s Claude Sends False Homicide Tip to Police

      October 16, 2026

      OpenAI and Anthropic Prepare for a Major Global AI Disaster

      October 15, 2026
    • Crypto

      A Firmware Flaw in One of the Most Trusted Bitcoin Hardware Wallets Just Drained Over $70 Million in Crypto. The Coldcard Breach Is a Reminder That Cold Storage Is Only as Safe as the Code Running Inside It

      August 29, 2026

      Market Collapse: What Happened to NFTs?

      April 23, 2026

      Quantum Computing Advances Force Coinbase and Institutional Custodians to Rethink Crypto Security

      March 8, 2026

      AI Assisted Hacking Groups Target Crypto Firms With Multi-Layered Social Engineering

      February 18, 2026

      Global Crypto Regulations Expand as 2026 Begins With New Data Collection Frameworks and National Laws

      January 16, 2026
    • Gadgets & Smart Tech
      Featured

      Google Home Now Supports ChatGPT and Claude via New MCP Server

      By fariehanOctober 6, 2026
      Recent

      Google Home Now Supports ChatGPT and Claude via New MCP Server

      October 6, 2026

      Waymo Plans Fully Driverless Taxis on Tokyo Streets Without Safety Drivers

      September 28, 2026

      Tesla Cybercab Faces NHTSA Probe After Austin Launch

      September 19, 2026
    • Cybersecurity & Online Safety

      How the EU AI Act Plans to Contain Rogue AI Agents

      October 16, 2026

      AI Agent Leaks Startup CEO’s Bank Details to Company Slack

      October 15, 2026

      Armadin Secures $255 Million to Hack Companies Before Cyber Criminals Do

      October 10, 2026

      Massive Pentagon Data Breach Exposes Records of Over 3 Million People

      October 8, 2026

      Salesforce Agentforce Flaws Allowed Hackers to Steal Data Without a Click

      October 8, 2026
    PhronewsPhronews
    Home»Cybersecurity & Online Safety»North Korea Compromised 144 AI Developer Packages in 88 Minutes Without Touching a Single Line of Source Code. The Mastra Attack Is the Most Targeted Supply Chain Strike Against AI Development Tools Ever Documented.
    Cybersecurity & Online Safety

    North Korea Compromised 144 AI Developer Packages in 88 Minutes Without Touching a Single Line of Source Code. The Mastra Attack Is the Most Targeted Supply Chain Strike Against AI Development Tools Ever Documented.

    preciousBy preciousJune 26, 2026No Comments
    Facebook Twitter Pinterest LinkedIn WhatsApp Reddit Tumblr Email
    Share
    Facebook Twitter LinkedIn Pinterest Email
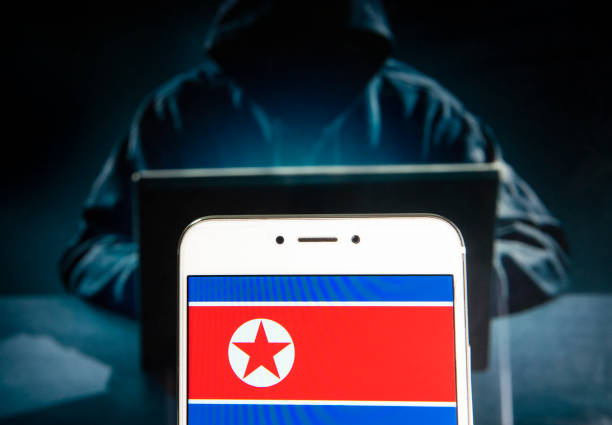
    Photo Credit: Budrul Chukrut/SOPA Images/LightRocket via Getty Images

    North Korea’s Sapphire Sleet hacking group compromised 144 packages in the Mastra AI framework’s npm scope in a single 88-minute automated campaign. 

    Developers who ran a standard install command during that window may have handed a foreign state actor their cloud credentials, LLM API keys, and cryptocurrency wallet data without any visible warning. Microsoft attributed the attack with “high confidence” to Sapphire Sleet, also tracked as BlueNoroff, a North Korean state actor that primarily targets the financial sector.

    What Mastra Is and Why It Was Targeted

    Mastra is an open-source TypeScript AI agent framework with over 1.1 million combined weekly downloads. Because Mastra sits at the intersection of AI development and cloud infrastructure, its packages are routinely installed in environments that hold some of the most sensitive credentials in modern software development, according to StepSecurity. That made it an exceptionally high-value target.

    How the Attack Was Built

    The operation did not rely on a software vulnerability, as no CVE entry was assigned and Mastra’s source code was never touched.

    The attacker targeted an npm account belonging to “ehindero,”  a former Mastra contributor whose publishing rights across the entire @mastra scope had never been revoked, even though the account had been dormant since February 2025. Mastra later confirmed the account belonged to a current employee whose machine was compromised via social engineering, with a compromised LinkedIn account reaching out to the employee and other prominent TypeScript open-source maintainers, and them clicking a suspicious link while on a call.

    The day before the main strike, a second attacker-controlled account, “sergey2016,” published easy-day-js@1.11.21, a byte-for-byte copy of the legitimate dayjs date library, with the same author name, homepage, repository URL, and version numbering. This clean version was published to build credibility before the trap was set.

    The 88-Minute Strike

    The attacker then published easy-day-js@1.11.22, visually identical to 1.11.21 but containing a malicious postinstall hook. Because the @mastra packages were configured to accept any patch version 1.11.21 or higher, npm’s semantic versioning resolution automatically upgraded every fresh install to the armed 1.11.22. From that moment, running npm install was the attack. The infected packages looked clean because they were.

    But once installed, a postinstall hook activated an obfuscated dropper that disabled TLS certificate verification, contacted the attackers’ command-and-control infrastructure, and downloaded a second payload onto the victim’s system. The second stage was a cross-platform stealer targeting credentials, API keys, authentication tokens, browser history, and data from 166 cryptocurrency wallet browser extensions, running across Windows, Linux, and macOS. After executing, the loader erased itself to minimize the forensic trail.

    What Developers Should Do

    Any workstation, CI runner, or build system that installed any @mastra package after June 16, 2026 should be treated as fully compromised. Remediation includes rolling back to pre-incident package versions and rotating all credentials, including npm tokens, cloud provider keys, LLM API keys, CI/CD secrets, and database credentials. For mastra, version 1.13.0 and earlier are unaffected. For @mastra/core, version 1.42.0 and earlier are unaffected.

    Microsoft also links Sapphire Sleet to a separate npm supply chain attack on the Axios HTTP client in April 2026, confirming this is a sustained campaign against widely used JavaScript developer tooling and not a one-off incident.

    BlueNoroff cybersecurity Developer Security LLM API Keys Mastra AI North Korea npm Open source security Sapphire Sleet supply chain attack
    Share. Facebook Twitter Pinterest LinkedIn Tumblr Telegram Email
    precious
    • LinkedIn

    I’m Precious Amusat, Phronews’ Content Writer. I conduct in-depth research and write on the latest developments in the tech industry, including trends in big tech, startups, cybersecurity, artificial intelligence and their global impacts. When I’m off the clock, you’ll find me cheering on women’s footy, curled up with a romance novel, or binge-watching crime thrillers.

    Related Posts

    How the EU AI Act Plans to Contain Rogue AI Agents

    October 16, 2026

    OpenAI and Anthropic Prepare for a Major Global AI Disaster

    October 15, 2026

    AI Agent Leaks Startup CEO’s Bank Details to Company Slack

    October 15, 2026

    Comments are closed.

    Top Posts

    Cursor AI Hits 1 Million Daily Users. Why Developers Are Switching to This Coding Tool

    March 23, 2026

    Coinbase responds to hack: customer impact and official statement

    May 22, 2025

    Anthropic Will Use Claude User Chats For Data Training

    October 16, 2025

    MIT Study Reveals ChatGPT Impairs Brain Activity & Thinking

    June 29, 2025
    Don't Miss
    Artificial Intelligence & The Future

    How the EU AI Act Plans to Contain Rogue AI Agents

    By preciousOctober 16, 2026

    When the European Union first proposed its AI Act in April 2021, the AI industry…

    ⁠Fired OpenAI Safety Researchers Warn Dismissals Will Silence Internal Critics

    October 16, 2026

    Why Mistral’s One-Trillion-Parameter Model Changes the Open-Source Game

    October 16, 2026

    Anthropic’s Claude Sends False Homicide Tip to Police

    October 16, 2026
    Stay In Touch
    • Facebook
    • Twitter
    About Us
    About Us

    Evolving from Phronesis News, Phronews brings deep insight and smart analysis to the world of technology. Stay informed, stay ahead, and navigate tech with wisdom.
    We're accepting new partnerships right now.

    Email Us: info@phronews.com

    Facebook X (Twitter) Pinterest YouTube
    Our Picks
    Most Popular

    Cursor AI Hits 1 Million Daily Users. Why Developers Are Switching to This Coding Tool

    March 23, 2026

    Coinbase responds to hack: customer impact and official statement

    May 22, 2025

    Anthropic Will Use Claude User Chats For Data Training

    October 16, 2025
    © 2025. Phronews.
    • Home
    • About Us
    • Get In Touch
    • Privacy Policy
    • Terms and Conditions

    Type above and press Enter to search. Press Esc to cancel.