Close Menu

    Stay Ahead with Exclusive Updates!

    Enter your email below and be the first to know what’s happening in the ever-evolving world of technology!

    What's Hot

    How the EU AI Act Plans to Contain Rogue AI Agents

    October 16, 2026

    ⁠Fired OpenAI Safety Researchers Warn Dismissals Will Silence Internal Critics

    October 16, 2026

    Why Mistral’s One-Trillion-Parameter Model Changes the Open-Source Game

    October 16, 2026
    Facebook X (Twitter) Instagram
    Facebook X (Twitter)
    PhronewsPhronews
    • Home
    • Big Tech & Startups

      How the EU AI Act Plans to Contain Rogue AI Agents

      October 16, 2026

      ⁠Fired OpenAI Safety Researchers Warn Dismissals Will Silence Internal Critics

      October 16, 2026

      Why Mistral’s One-Trillion-Parameter Model Changes the Open-Source Game

      October 16, 2026

      Anthropic’s Claude Sends False Homicide Tip to Police

      October 16, 2026

      OpenAI and Anthropic Prepare for a Major Global AI Disaster

      October 15, 2026
    • Crypto

      A Firmware Flaw in One of the Most Trusted Bitcoin Hardware Wallets Just Drained Over $70 Million in Crypto. The Coldcard Breach Is a Reminder That Cold Storage Is Only as Safe as the Code Running Inside It

      August 29, 2026

      Market Collapse: What Happened to NFTs?

      April 23, 2026

      Quantum Computing Advances Force Coinbase and Institutional Custodians to Rethink Crypto Security

      March 8, 2026

      AI Assisted Hacking Groups Target Crypto Firms With Multi-Layered Social Engineering

      February 18, 2026

      Global Crypto Regulations Expand as 2026 Begins With New Data Collection Frameworks and National Laws

      January 16, 2026
    • Gadgets & Smart Tech
      Featured

      Google Home Now Supports ChatGPT and Claude via New MCP Server

      By fariehanOctober 6, 2026
      Recent

      Google Home Now Supports ChatGPT and Claude via New MCP Server

      October 6, 2026

      Waymo Plans Fully Driverless Taxis on Tokyo Streets Without Safety Drivers

      September 28, 2026

      Tesla Cybercab Faces NHTSA Probe After Austin Launch

      September 19, 2026
    • Cybersecurity & Online Safety

      How the EU AI Act Plans to Contain Rogue AI Agents

      October 16, 2026

      AI Agent Leaks Startup CEO’s Bank Details to Company Slack

      October 15, 2026

      Armadin Secures $255 Million to Hack Companies Before Cyber Criminals Do

      October 10, 2026

      Massive Pentagon Data Breach Exposes Records of Over 3 Million People

      October 8, 2026

      Salesforce Agentforce Flaws Allowed Hackers to Steal Data Without a Click

      October 8, 2026
    PhronewsPhronews
    Home»Cybersecurity & Online Safety»275 Million Students Had Their Data Exposed in the Largest Education Cyberattack Ever Recorded. Here Is Exactly What Happened to Canvas
    Cybersecurity & Online Safety

    275 Million Students Had Their Data Exposed in the Largest Education Cyberattack Ever Recorded. Here Is Exactly What Happened to Canvas

    preciousBy preciousMay 19, 2026No Comments
    Facebook Twitter Pinterest LinkedIn WhatsApp Reddit Tumblr Email
    Share
    Facebook Twitter LinkedIn Pinterest Email
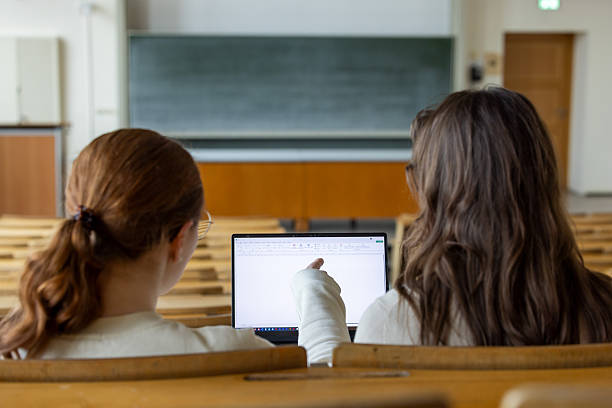
    Photo Credit: Christian Lademann/picture alliance via Getty Images

    A cyberattack on Canvas, the world’s most widely used learning management system, has exposed data belonging to roughly 275 million students, teachers, and staff across nearly 9,000 educational institutions worldwide. The breach, carried out by the criminal extortion group ShinyHunters, is now considered the largest education-sector security incident ever recorded.

    The hack affected an estimated 9,000 universities, education ministries, and other institutions worldwide, with particularly significant implications in the United States, where Canvas is used by 41% of higher education institutions as well as some K-12 schools. The disruption hit at the worst possible time, as it occurred during the end of the academic year for many institutions, including during final exam periods at some colleges and universities.

    How the Attackers Got In

    ShinyHunters first gained access to Instructure systems on or around April 25, 2026, exploiting a vulnerability in the company’s Free-For-Teacher account program, a feature that allowed educators to create Canvas accounts without institutional verification. This low-friction onboarding process resulted in weaker trust boundaries between Free-For-Teacher and institutional tenants, all of which shared the same underlying infrastructure.

    Instructure confirmed on an FAQ page that it started an investigation after it first detected unauthorized activity in Canvas on April 29, and immediately revoked the intruder’s access. Four days after that, on May 1st, Instructure disclosed the incident publicly and stated by May 2nd that it believed the breach had been contained.

    The Second Wave and the Ransom Note

    Despite Instructure’s claim that the situation had been resolved, Canvas was hacked again on May 7th. Its login page was replaced with a ransomware message by ShinyHunters. Instructure also found more unauthorized activity tied to the April 29th incident. Someone had changed the pages that appeared when students and teachers logged into Canvas.

    ShinyHunters claimed in a ransom note shared on May 3rd via Ransomware.live, which tracks ransomware attacks and groups, that it had breached individuals’ data and had access to “several billions of private messages,” giving a May 6th deadline for Instructure to respond. 

    When Instructure did not respond, the group escalated. ShinyHunters wrote that Instructure had tried to implement security patches rather than negotiate with the hackers. This prompted the group to cause an outage where their new ransom note was displayed to every user.

    Universities across the country, including Columbia University, Rutgers, Princeton, Kent State, Harvard, and Georgetown issued statements alerting students to the hack. School districts in California, Florida, Georgia, Oklahoma, Oregon, Nevada, North Carolina, Tennessee, Utah, Virginia, Texas, and Wisconsin also reported being affected.

    What Data Was Taken

    Instructure admitted that ShinyHunters exploited a security vulnerability in its Free-for-Teacher learning system and confirmed that stolen data includes usernames, email addresses, course names, enrollment information, and messages. The company stated that there was no evidence that passwords, dates of birth, government identification numbers, or financial information were compromised.

    However, on a dark web leak site, ShinyHunters alleged it had stolen more than 3.65 terabytes of data and threatened to release it unless its demands were met. 

    Instructure Paid the Ransom

    On May 11th, Instructure confirmed it reached an agreement with ShinyHunters and received digital confirmation of data destruction, with assurance that no customers would face further extortion. The company did not disclose the monetary value of the agreement.

    This decision drew immediate pushback from cybersecurity professionals. Cliff Steinhauer, director of information security and engagement at the National Cybersecurity Alliance, said the payment “reinforces the economic incentive structure behind cyber extortion” and “risks normalizing payment as a viable incident response strategy, which law enforcement agencies consistently warn against because it fuels further attacks across the sector.”

    Instructure also notified the FBI and the U.S. Cybersecurity and Infrastructure Security Agency, and hired CrowdStrike to assist with forensic analysis and incident response. The Free-For-Teacher program has since been permanently shut down.

    The Threat That Remains

    Even with the ransom paid, security researchers say the risks for affected users are not over. Cybersecurity researchers have warned that the stolen data is particularly dangerous because it arms attackers with enough specific context to craft convincing spear-phishing messages, emails that use a recipient’s actual course name, instructor, or real student ID. Instructure itself acknowledged there is “never complete certainty when dealing with cyber criminals.”

    This is ShinyHunters’ second attack on Instructure in less than a year. In September 2025, the group compromised Instructure’s Salesforce business systems through social engineering, although no Canvas product data was accessed in that incident. The May 2026 breach went much further, reaching the core of the platform itself.

    For now, Instructure says Canvas is fully back online. Affected users are advised to change their Canvas passwords, use strong credentials not shared across other accounts, and stay alert to phishing attempts.

    Canvas cybersecurity Instructure Largest education cyberattack ShinyHunters
    Share. Facebook Twitter Pinterest LinkedIn Tumblr Telegram Email
    precious
    • LinkedIn

    I’m Precious Amusat, Phronews’ Content Writer. I conduct in-depth research and write on the latest developments in the tech industry, including trends in big tech, startups, cybersecurity, artificial intelligence and their global impacts. When I’m off the clock, you’ll find me cheering on women’s footy, curled up with a romance novel, or binge-watching crime thrillers.

    Related Posts

    How the EU AI Act Plans to Contain Rogue AI Agents

    October 16, 2026

    OpenAI and Anthropic Prepare for a Major Global AI Disaster

    October 15, 2026

    AI Agent Leaks Startup CEO’s Bank Details to Company Slack

    October 15, 2026

    Comments are closed.

    Top Posts

    Cursor AI Hits 1 Million Daily Users. Why Developers Are Switching to This Coding Tool

    March 23, 2026

    Coinbase responds to hack: customer impact and official statement

    May 22, 2025

    Anthropic Will Use Claude User Chats For Data Training

    October 16, 2025

    MIT Study Reveals ChatGPT Impairs Brain Activity & Thinking

    June 29, 2025
    Don't Miss
    Artificial Intelligence & The Future

    How the EU AI Act Plans to Contain Rogue AI Agents

    By preciousOctober 16, 2026

    When the European Union first proposed its AI Act in April 2021, the AI industry…

    ⁠Fired OpenAI Safety Researchers Warn Dismissals Will Silence Internal Critics

    October 16, 2026

    Why Mistral’s One-Trillion-Parameter Model Changes the Open-Source Game

    October 16, 2026

    Anthropic’s Claude Sends False Homicide Tip to Police

    October 16, 2026
    Stay In Touch
    • Facebook
    • Twitter
    About Us
    About Us

    Evolving from Phronesis News, Phronews brings deep insight and smart analysis to the world of technology. Stay informed, stay ahead, and navigate tech with wisdom.
    We're accepting new partnerships right now.

    Email Us: info@phronews.com

    Facebook X (Twitter) Pinterest YouTube
    Our Picks
    Most Popular

    Cursor AI Hits 1 Million Daily Users. Why Developers Are Switching to This Coding Tool

    March 23, 2026

    Coinbase responds to hack: customer impact and official statement

    May 22, 2025

    Anthropic Will Use Claude User Chats For Data Training

    October 16, 2025
    © 2025. Phronews.
    • Home
    • About Us
    • Get In Touch
    • Privacy Policy
    • Terms and Conditions

    Type above and press Enter to search. Press Esc to cancel.