Close Menu

    Stay Ahead with Exclusive Updates!

    Enter your email below and be the first to know what’s happening in the ever-evolving world of technology!

    What's Hot

    Nvidia and Oracle Shares Sink Following Shocking OpenAI Revenue Report

    October 21, 2026

    Chinese Hacker Weaponizes Claude AI to Breach South Korean Banks

    October 19, 2026

    Apple Slashes iPhone 18 Pro Orders by 15% as Demand Softens

    October 19, 2026
    Facebook X (Twitter) Instagram
    Facebook X (Twitter)
    PhronewsPhronews
    • Home
    • Big Tech & Startups

      Nvidia and Oracle Shares Sink Following Shocking OpenAI Revenue Report

      October 21, 2026

      Apple Slashes iPhone 18 Pro Orders by 15% as Demand Softens

      October 19, 2026

      Weak Enterprise AI Data Controls Fuel MIND Security’s $72M Funding Raise

      October 18, 2026

      OpenAI Dots Gives ChatGPT Always-On Agents With Dedicated Cloud Computers

      October 18, 2026

      How the EU AI Act Plans to Contain Rogue AI Agents

      October 16, 2026
    • Crypto

      A Firmware Flaw in One of the Most Trusted Bitcoin Hardware Wallets Just Drained Over $70 Million in Crypto. The Coldcard Breach Is a Reminder That Cold Storage Is Only as Safe as the Code Running Inside It

      August 29, 2026

      Market Collapse: What Happened to NFTs?

      April 23, 2026

      Quantum Computing Advances Force Coinbase and Institutional Custodians to Rethink Crypto Security

      March 8, 2026

      AI Assisted Hacking Groups Target Crypto Firms With Multi-Layered Social Engineering

      February 18, 2026

      Global Crypto Regulations Expand as 2026 Begins With New Data Collection Frameworks and National Laws

      January 16, 2026
    • Gadgets & Smart Tech
      Featured

      Apple Slashes iPhone 18 Pro Orders by 15% as Demand Softens

      By preciousOctober 19, 2026
      Recent

      Apple Slashes iPhone 18 Pro Orders by 15% as Demand Softens

      October 19, 2026

      Google Home Now Supports ChatGPT and Claude via New MCP Server

      October 6, 2026

      Waymo Plans Fully Driverless Taxis on Tokyo Streets Without Safety Drivers

      September 28, 2026
    • Cybersecurity & Online Safety

      Chinese Hacker Weaponizes Claude AI to Breach South Korean Banks

      October 19, 2026

      ASOS App Alerts Hijacked in Massive Customer Data Breach

      October 18, 2026

      Denmark Population Register Hacked, Exposing 8.8 Million Citizen Records

      October 18, 2026

      How the EU AI Act Plans to Contain Rogue AI Agents

      October 16, 2026

      AI Agent Leaks Startup CEO’s Bank Details to Company Slack

      October 15, 2026
    PhronewsPhronews
    Home»Cybersecurity & Online Safety»Ransomware Terror: How SafePay Hijacked Ingram Micro
    Cybersecurity & Online Safety

    Ransomware Terror: How SafePay Hijacked Ingram Micro

    oluchiBy oluchiJuly 15, 2025Updated:July 15, 2025No Comments
    Facebook Twitter Pinterest LinkedIn WhatsApp Reddit Tumblr Email
    Share
    Facebook Twitter LinkedIn Pinterest Email
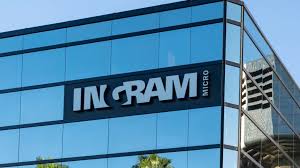
    Image Generated from IT Daily

    SafePay ransomware, which brought Ingram Micro’s global order systems to a grinding halt, served as a jarring reminder of rising cyber threats in the IT supply chain. The disruption affected thousands of resellers and managed service providers, underscoring the vulnerabilities in third-party platforms and the urgent need for cyber resilience.

    Ingram Micro is one of the world’s largest business-to-business technology distributors and service providers. They serve as a vital link between technology manufacturers and the businesses that sell and implement those technologies. Let’s take a deep dive into its ransomware situation and impact.

    Who is SafePay?

    SafePay is a ransomware attack group that has been in operation since late 2024. The group has since made headlines as one of the most active ransomware groups globally. 

    They have since claimed credit for over 200 ransomware attacks that occurred from late 2024 until July 2025. Their modus operandi:

    • Exploit VPN credentials or vulnerabilities in the network about to be hacked.
    • Gain initial access, then deploy malware to encrypt their victim’s systems.
    • Exfiltrate sensitive data
    • Threaten public data leaks unless a ransom is paid

    What Happened? 

    According to BleepingComputer, it was initially believed the ransomware used by the attackers gained access to Ingram Micro’s internal system through Palo Alto’s GlobalProtect VPN gateway through compromised credentials. 

    The claim was later debunked by Palo Alto Networks that their VPN was not the source of vulnerability for the breach.

    Although it is not fully clear as to how the ransomware gained access to Ingram Micro’s system, as investigations are ongoing, here’s what we know happened in relation to the attack:

    • The attack occurred in the early hours of Thursday, July 3, with employees finding ransom notes on their devices. 
    • The ransom note was identified as one of SafePay’s strategies, as it bore similar markers with notes used in other attacks by the cyber group.
    • On July 4, the company recognized the severity of the situation, and proactive measures were taken to shut down the system, causing a global blackout to contain the spread of the ransomware. 
    • The shutdown included critical platforms like their Xvantage distribution platform and Impulse license provisioning system vital for order processing, software licensing, and partner services.
    • On July 5, the company announced officially that it had identified ransomware on its internal system.
    • Early reports speculated the attackers gained access through the company’s GlobalProtect VPN; however, this was not confirmed by Ingram Micro, and later it was debunked by Palo Alto (Ingram Micro’s partner and owner/developer of GlobalProtect VPN).
    • From July 7 to 9, the company began phased restoration of its systems, with the company going back to full operational capabilities globally by 9:50 PT on July 9.
    • It is speculated that SafePay was behind the ransomware attack due to the markers in the ransom note sent. SafePay, however, has not taken credit for the attack, and Ingram Micro has not verified it was done by them.

    The impact following the attack was severe on a global scale due to delayed order processing, significant shipment backlogs, and interruptions in software licensing across popular platforms like Microsoft 365 and Dropbox. This not only led to financial loss for Ingram Micro and its partners but also has temporarily damaged Ingram’s reputation for supply chain reliability.

    A Wake-up Call for Businesses Worldwide

    Although investigations are still ongoing regarding circumstances regarding the attack, and operations at Ingram Micro are back to normal, the ransomware incident serves as a stark warning to organizations of all sizes.

    Organizations in the supply chain industry are implored to take steps to bolster cybersecurity defense systems. Here are key takeaways to be learned and implemented:

    • Harden Remote Access Infrastructure: although a compromised VPN was not confirmed to be the entry point for this attack, it is one commonly used by ransomware groups like Safepay.

    Measures should be taken to secure your VPN gateways with robust configurations and enforce strong authentication, especially Multi-Factor Authentication (MFA), for all remote access and privileged accounts. 

    • Network Segmentation: segmenting your network will limit movement by attackers even if they breach an initial point.
    • Incident Response Plan: develop and regularly have drills for a comprehensive incident response plan. Knowing what to do before an attack happens can significantly lessen the damage.
    • Employee Training: human error is a significant vulnerability, and it will always remain so. To get around this, employees should have regular workshops on how to identify phishing attacks, social engineering, and the importance of strong security practices.
    • Robust Backup and Recovery: Having an immutable and up-to-date backup system is a last line of defense against data loss due to ransomware.

    By prioritizing cyber resilience and staying vigilant against evolving attack techniques, businesses can better protect their operations and reduce the rate of ransomware attacks on a global scale.

    Backup and recovery systems Business tech disruption Cyber resilience tips Cyber threat warning Cyberattack recovery Cybercrime group 2025 cybersecurity breach Employee cybersecurity training Global ransomware impact globalProtect VPN Globalprotect vpn security Impulse license system Incident response plan Ingram Micro Ingram micro cyberattack Ingram micro systems down It supply chain threat multifactor authentication Network segmentation tips Palo alto vpn controversy Ransom note markers ransomware attack Ransomware attack 2025 Ransomware entry points SafePay ransomware Supply Chain Supply chain cybersecurity Third-party platform security Xvantage platform outage
    Share. Facebook Twitter Pinterest LinkedIn Tumblr Telegram Email
    oluchi
    • X (Twitter)
    • LinkedIn

    I am a content writer with over three years of experience. I specialize in creating clear, engaging, and value-driven content across diverse niches, and I’m now focused on the tech and business space. My strong research skills, paired with a natural storytelling ability, enable me to break down complex topics into compelling, reader-friendly articles. As an avid reader and music lover, I bring creativity, insight, and a sharp eye for detail to every piece I write.

    Related Posts

    Chinese Hacker Weaponizes Claude AI to Breach South Korean Banks

    October 19, 2026

    Apple Slashes iPhone 18 Pro Orders by 15% as Demand Softens

    October 19, 2026

    ASOS App Alerts Hijacked in Massive Customer Data Breach

    October 18, 2026

    Comments are closed.

    Top Posts

    Cursor AI Hits 1 Million Daily Users. Why Developers Are Switching to This Coding Tool

    March 23, 2026

    Coinbase responds to hack: customer impact and official statement

    May 22, 2025

    Anthropic Will Use Claude User Chats For Data Training

    October 16, 2025

    MIT Study Reveals ChatGPT Impairs Brain Activity & Thinking

    June 29, 2025
    Don't Miss
    Big Tech & Startups

    Nvidia and Oracle Shares Sink Following Shocking OpenAI Revenue Report

    By preciousOctober 21, 2026

    Many artificial intelligence hardware and cloud companies rely on massive multiyear contracts with top software…

    Chinese Hacker Weaponizes Claude AI to Breach South Korean Banks

    October 19, 2026

    Apple Slashes iPhone 18 Pro Orders by 15% as Demand Softens

    October 19, 2026

    ASOS App Alerts Hijacked in Massive Customer Data Breach

    October 18, 2026
    Stay In Touch
    • Facebook
    • Twitter
    About Us
    About Us

    Evolving from Phronesis News, Phronews brings deep insight and smart analysis to the world of technology. Stay informed, stay ahead, and navigate tech with wisdom.
    We're accepting new partnerships right now.

    Email Us: info@phronews.com

    Facebook X (Twitter) Pinterest YouTube
    Our Picks
    Most Popular

    Cursor AI Hits 1 Million Daily Users. Why Developers Are Switching to This Coding Tool

    March 23, 2026

    Coinbase responds to hack: customer impact and official statement

    May 22, 2025

    Anthropic Will Use Claude User Chats For Data Training

    October 16, 2025
    © 2025. Phronews.
    • Home
    • About Us
    • Get In Touch
    • Privacy Policy
    • Terms and Conditions

    Type above and press Enter to search. Press Esc to cancel.